Hackers Turn AOMEI Update Servers Into Malware Channels - BankInfoSecurity
This story deserves to be shared
Send it to someone who'd care, or post it on your networks.
This article is an excerpt. To read the full content, visit the original source. BankInfoSecurity
Related articles
Insurer secures hybrid cloud with 99.8% malware block rate - DXC Technology
325-year old insurer achieves 99.8% malware protection What does it take to help one of North America's leading insurers, with a heritage spanning centuries and millions of customers, accelerate its digital transformation journey? That was the question facing a leading property and casualty insurer. The company had deep financial roots and trusted relationships — but modernizing its IT infrastructure while keeping data safe across hybrid cloud environments was a high-stakes balancing act.
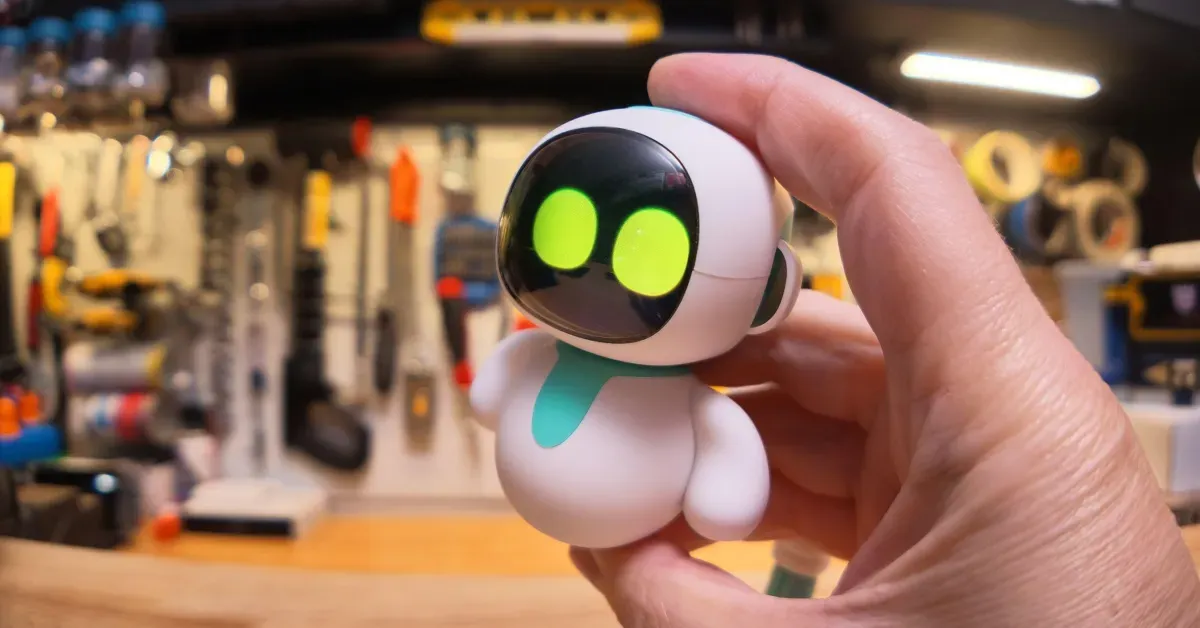
Your secrets aren’t safe with this cute robot toy — they’re on Chinese servers ready to be hacked - The Verge
There’s a new digital pet in town — a cute little marshmallow of a robot that can change its cartoony expressions to match your mood. But if you or your kids talk to “Eiliko” over Wi-Fi, it’ll phone home to China. Its AI companion can store literally everything you tell it on Chinese servers, where hackers can easily gain access or even hijack its personality. And the company that made it, Energize Lab, doesn’t seem to care. I bought an Eiliko from Amazon on August 29th. During a 10-minute conversation on August 30th, I asked the little bot: “Do you ever tell anybody else what I’m saying?”“Your secrets are safe with me,” it replied. Within minutes, a man on the other side of the planet had a complete transcript of everything I’d told the toy. Photo by Sean Hollister / The VergeHe didn’t just have my conversations, either. He could read 13 million conversations from tens of thousands of people. He could access seemingly the entire active worldwide fleet of 68,000 robot toys. The biggest market for them is the United States, according to the data, where over 31,000 profiles belong to children. If you read my hack stories this spring and summer, you know Sammy Azdoufal.
How Israeli firm’s ‘zero-click’ malware attack poses global security risk - Al Jazeera
Just visiting a page or refreshing an app can be enough to fall victim to a malware attack in which your personal data is stolen from a laptop or phone, researchers have found. You are not even required to “click” on anything. An Israeli spyware firm has been found to be behind the first-known instance of “zero-click” targeted advertising in which fraudsters or spies can steal private data and send it to external servers, with Al Jazeera journalists among the victims. Recommended Stories list of 3 itemslist 1 of 3A world on trial: How lawyers documenting Israeli abuse pay a pricelist 2 of 3EU lawmaker investigating surveillance hacked by Israeli spyware, report sayslist 3 of 3UK, US, Netherlands warn of Iran-linked spywareend of listIn June 2025, 45 devices used by Al Jazeera staff – including several who reported on sensitive subjects – were targeted with spyware which installed itself without the need to open or download any files. An investigation by the Canada-based academic research unit Citizen Lab, prompted by Al Jazeera’s initial internal probe into the issue, discovered that the Israeli company Candiru was behind the attacks.
0 comments
No comments yet. Be the first to share your thoughts!