The not-so-secret vulnerability in Ukraine’s drone arsenal? Chinese technology - Toronto Star
This story deserves to be shared
Send it to someone who'd care, or post it on your networks.
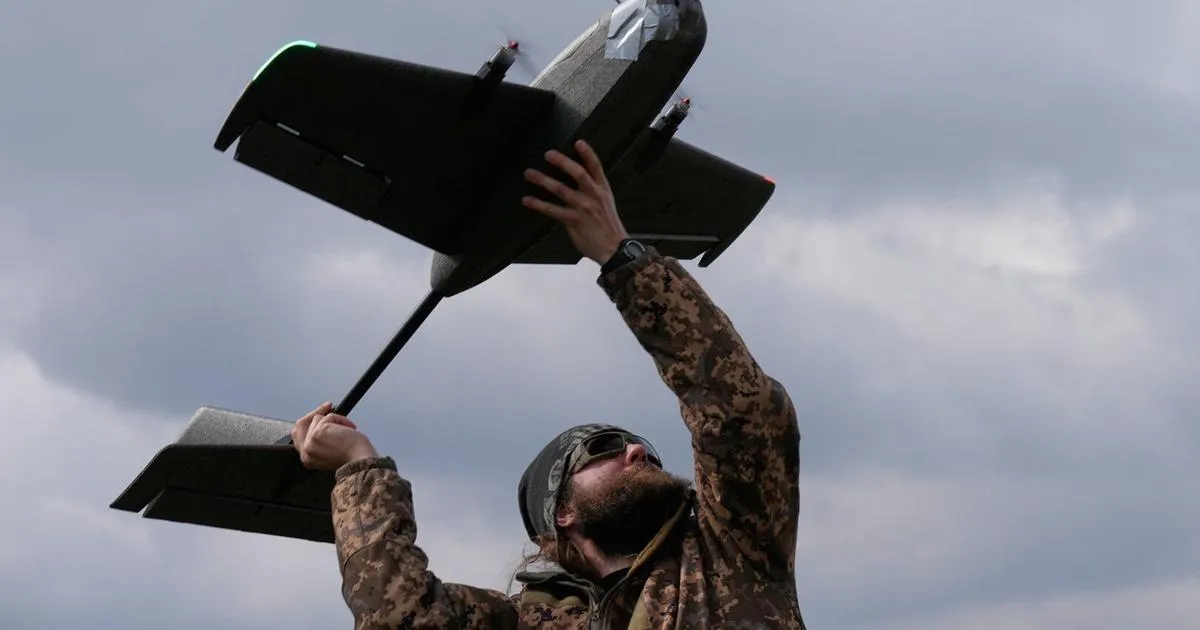
A student soldier of the Yatagan School for Unmanned Aerial Systems launches a training target drone during drills in the Kyiv region, Ukraine, Thursday, March 19, 2026. KYIV, Ukraine (AP) — Since Russia invaded more than four years ago, Ukraine has become a global leader in military drone innovation, enabling its forces to grind a much larger enemy to a stalemate. But this technological force multiplier has come with an unsettling vulnerability: Ukrainian drone makers are highly dependent on electronics made by China, a key Russian ally.
This article is an excerpt. To read the full content, visit the original source. Toronto Star
Related articles
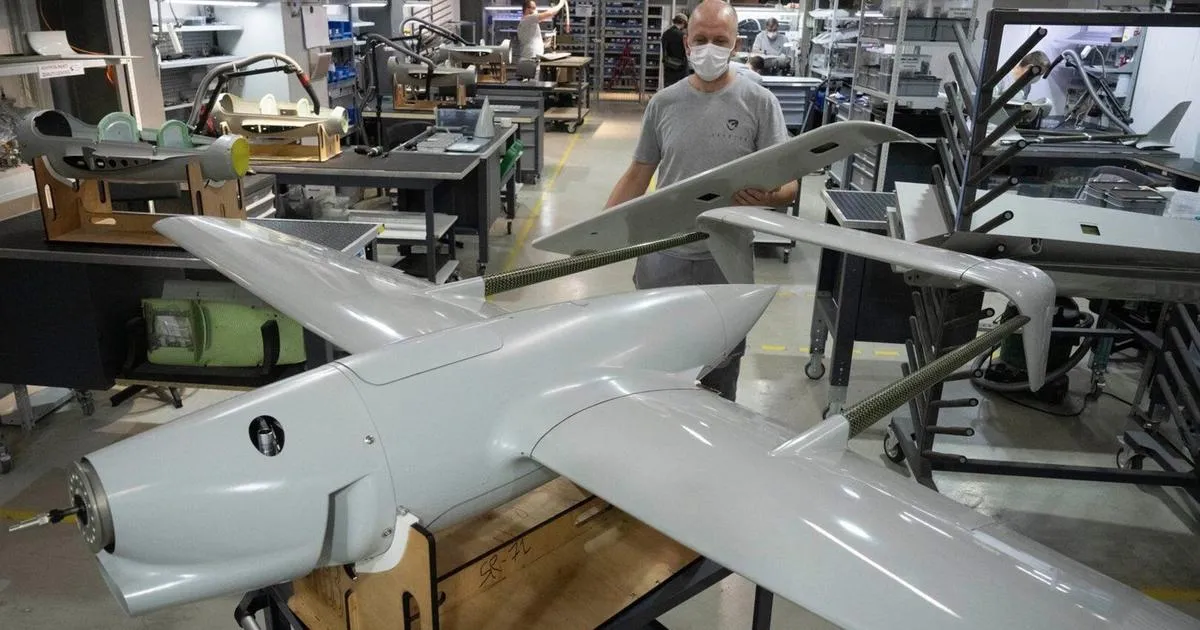
The not-so-secret vulnerability in Ukraine’s drone arsenal? Chinese technology - The Spec
KYIV, Ukraine (AP) — Since Russia invaded more than four years ago, Ukraine has become a global leader in military drone innovation, enabling its forces to grind a much larger
How AI vulnerability discovery is rapidly reshaping SOC reporting - EY
Shifting client and auditor expectations for SOC reporting Service organizations now face a shifting threat landscape. The assumption that an organization’s software is reasonably secure because it has traditional SOC reports and no major incidents have occurred may no longer be adequate as clients and regulators may question whether hidden vulnerabilities likely exist in the environment. Boards and audit committees are pressing organizational leaders for answers on how their service providers address AI’s ability to swiftly detect and exploit overlooked weaknesses.
Today’s NYT Strands Hints, Spangram and Answers for Sunday, Oct. 18, #959 - CNET
Here’s your NYT Strands hint for today, plus the spangram and all of today’s Strands answers for puzzle No. 959 on Sunday, Oct. 18, 2026. Today’s Strands theme was tricky. It helps to be a runner. Read on for all the answers.
WARNING: ConnectWise Supply-Chain Attack Exposes Microsoft 365 Tenants - LinkedIn
A supply-chain attack involving ConnectWise’s cloud services has exposed Microsoft 365 customers to unauthorized application access, with researchers reporting successful sign-ins across 173 partner and customer tenants. The incident centres on credentials associated with ConnectWise Cloud Backup, formerly SkyKick, and raises concerns about attackers exploiting permissions already entrusted to business software. ConnectWise has confirmed unauthorized access to application identities within its Cloud Backup environment. In an October 17 update on its service-status page, the company said it was shutting off application access, interrupting customer backups while investigation and remediation continued.
0 comments
No comments yet. Be the first to share your thoughts!