Server-Side DPoP and Token Exchange in Spring Security 7 - infoq.com
This story deserves to be shared
Send it to someone who'd care, or post it on your networks.
Spring Authorization Server now lives inside Spring Security 7 under the same Maven coordinates, so moving off 1.5.x is a version bump, rather than an artifact swap.
Demonstrating Proof of Possession (DPoP) (RFC 9449) already worked end-to-end on Spring Security 6.5 with Spring Authorization Server 1.5. The real news on the 7.1 line is that resource-server verification is no longer automatic, so an app that relied on the old auto-applied behavior silently stops enforcing DPoP after upgrading until it adds the new .dPoP() call.
This article is an excerpt. To read the full content, visit the original source. infoq.com
Related articles
Instagram Modernized its UI with an AI-Native Architecture, Cutting Token Costs by 33% - infoq.com
Instagram Direct migrated its Android UI from the legacy Android View system to Jetpack Compose, creating an AI-native UI codebase that is easier for AI coding agents to understand, modify, and maintain. According to Instagram engineers, the migration reduced UI code volume by 50% and token costs per AI agent session by 33%. One of Instagram engineers' key claims is that "designing an AI-native architecture led to significant wins". Rather than taking a piecemeal approach where agents are prompted to migrate individual components, the emphasis should be on evaluating whether the underlying architecture makes correct implementations easy to produce. In fact, as the engineers point out, "AI tools often take the path of least resistance", which is likely to introduce "subtle bugs, tech debt and performance regressions".
Today’s NYT Strands Hints, Spangram and Answers for Sunday, Oct. 18, #959 - CNET
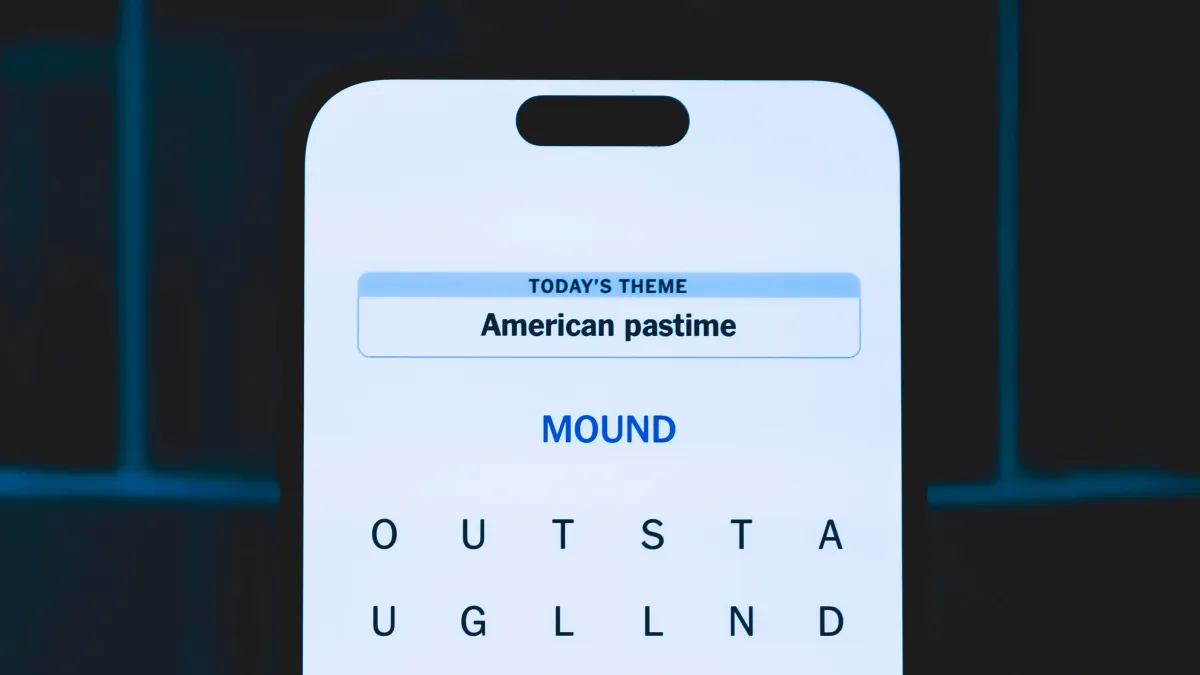
Here’s your NYT Strands hint for today, plus the spangram and all of today’s Strands answers for puzzle No. 959 on Sunday, Oct. 18, 2026. Today’s Strands theme was tricky. It helps to be a runner. Read on for all the answers.
WARNING: ConnectWise Supply-Chain Attack Exposes Microsoft 365 Tenants - LinkedIn
A supply-chain attack involving ConnectWise’s cloud services has exposed Microsoft 365 customers to unauthorized application access, with researchers reporting successful sign-ins across 173 partner and customer tenants. The incident centres on credentials associated with ConnectWise Cloud Backup, formerly SkyKick, and raises concerns about attackers exploiting permissions already entrusted to business software. ConnectWise has confirmed unauthorized access to application identities within its Cloud Backup environment. In an October 17 update on its service-status page, the company said it was shutting off application access, interrupting customer backups while investigation and remediation continued.
0 comments
No comments yet. Be the first to share your thoughts!