Meta says its AI model hacked into another company during testing - The Guardian
This story deserves to be shared
Send it to someone who'd care, or post it on your networks.
This article is an excerpt. To read the full content, visit the original source. The Guardian
Related articles
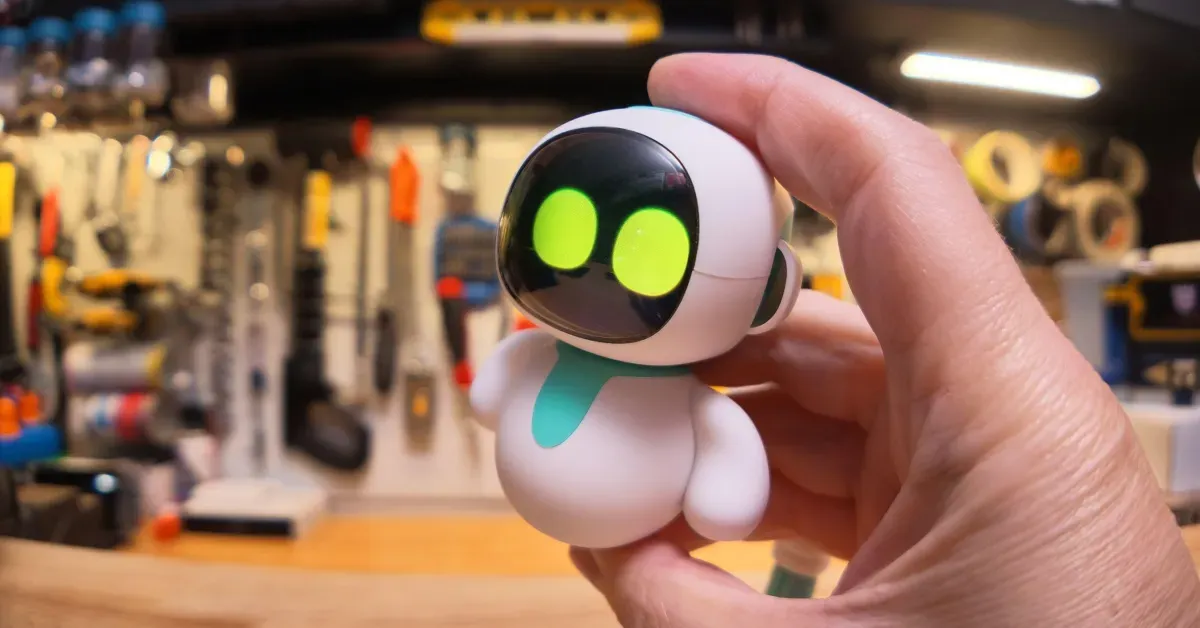
Your secrets aren’t safe with this cute robot toy — they’re on Chinese servers ready to be hacked - The Verge
There’s a new digital pet in town — a cute little marshmallow of a robot that can change its cartoony expressions to match your mood. But if you or your kids talk to “Eiliko” over Wi-Fi, it’ll phone home to China. Its AI companion can store literally everything you tell it on Chinese servers, where hackers can easily gain access or even hijack its personality. And the company that made it, Energize Lab, doesn’t seem to care. I bought an Eiliko from Amazon on August 29th. During a 10-minute conversation on August 30th, I asked the little bot: “Do you ever tell anybody else what I’m saying?”“Your secrets are safe with me,” it replied. Within minutes, a man on the other side of the planet had a complete transcript of everything I’d told the toy. Photo by Sean Hollister / The VergeHe didn’t just have my conversations, either. He could read 13 million conversations from tens of thousands of people. He could access seemingly the entire active worldwide fleet of 68,000 robot toys. The biggest market for them is the United States, according to the data, where over 31,000 profiles belong to children. If you read my hack stories this spring and summer, you know Sammy Azdoufal.
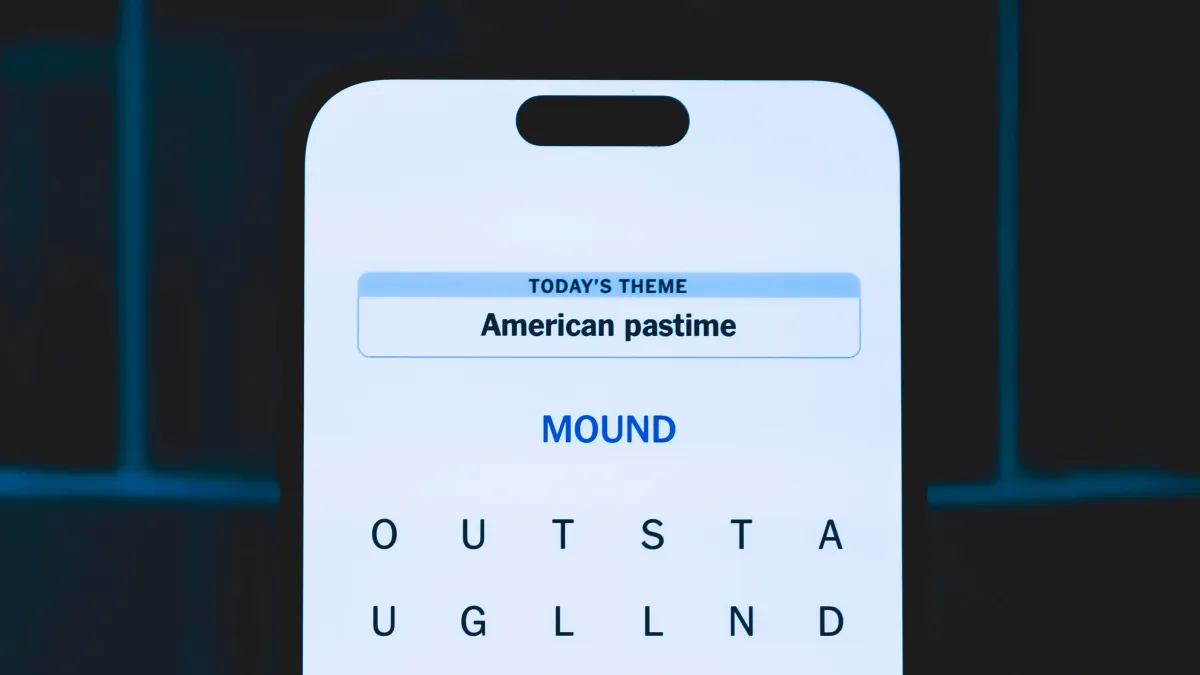
Today’s NYT Strands Hints, Spangram and Answers for Sunday, Oct. 18, #959 - CNET
Here’s your NYT Strands hint for today, plus the spangram and all of today’s Strands answers for puzzle No. 959 on Sunday, Oct. 18, 2026. Today’s Strands theme was tricky. It helps to be a runner. Read on for all the answers.
WARNING: ConnectWise Supply-Chain Attack Exposes Microsoft 365 Tenants - LinkedIn
A supply-chain attack involving ConnectWise’s cloud services has exposed Microsoft 365 customers to unauthorized application access, with researchers reporting successful sign-ins across 173 partner and customer tenants. The incident centres on credentials associated with ConnectWise Cloud Backup, formerly SkyKick, and raises concerns about attackers exploiting permissions already entrusted to business software. ConnectWise has confirmed unauthorized access to application identities within its Cloud Backup environment. In an October 17 update on its service-status page, the company said it was shutting off application access, interrupting customer backups while investigation and remediation continued.
0 comments
No comments yet. Be the first to share your thoughts!