Faith Hedgepeth Murder: New DNA technology linked defendant Miguel Salguero Olivares to key evidence, forensic scientist says - ABC11 News
This story deserves to be shared
Send it to someone who'd care, or post it on your networks.
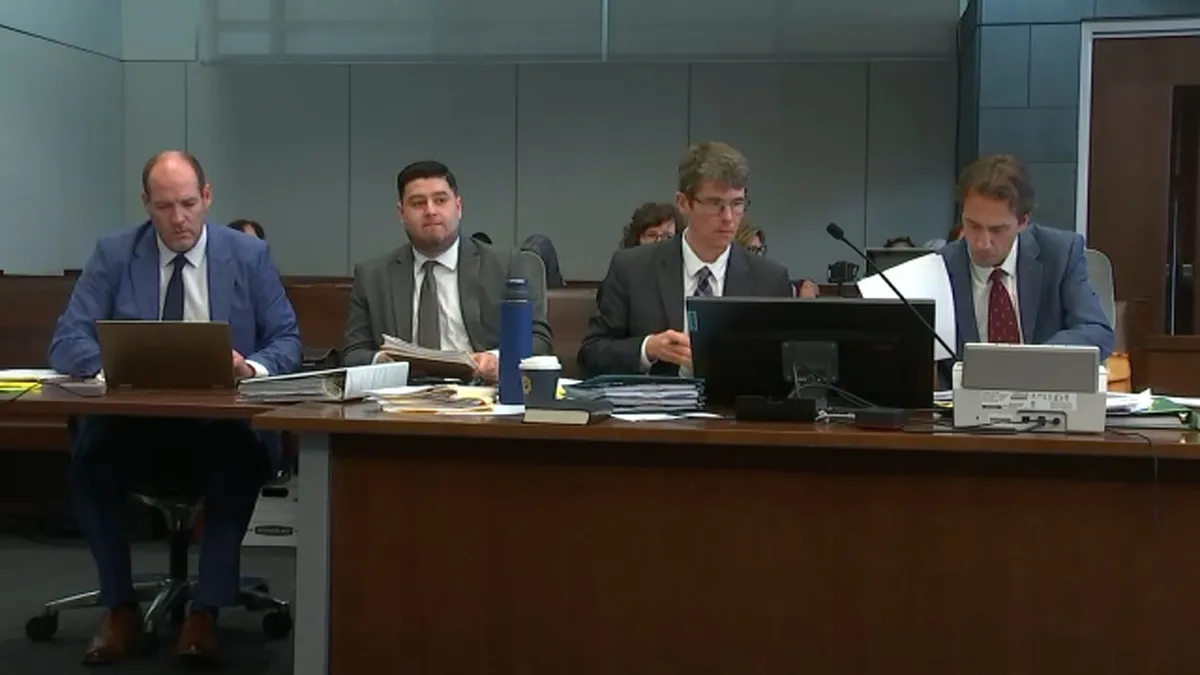
DURHAM, N. C. (WTVD) -- Jurors spent another day hearing detailed forensic testimony in the Faith Hedgepeth murder trial, with defense attorneys beginning their cross-examination of the state's DNA expert and focusing on what they contend were shortcomings in the handling and testing of evidence. Erin Ermish, a forensic scientist with the North Carolina State Crime Lab, was the only witness to testify Thursday. Ermish's role at the crime lab includes analyzing biological evidence such as blood, semen and saliva. She testified that she first examined evidence in the case in 2012, but re-examined several items in 2021 using updated DNA testing technology that allowed scientists to analyze additional portions of DNA profiles. According to Ermish, DNA profiles from a Bacardi rum bottle, a blue Riesling wine bottle, a white bag, Faith Hedgepeth's boxer shorts and samples collected from Hedgepeth's body included DNA from defendant Miguel Salguero Olivares. During direct examination, Ermish explained one of the DNA mixtures analyzed in the case.
This article is an excerpt. To read the full content, visit the original source. ABC11 News
Related articles
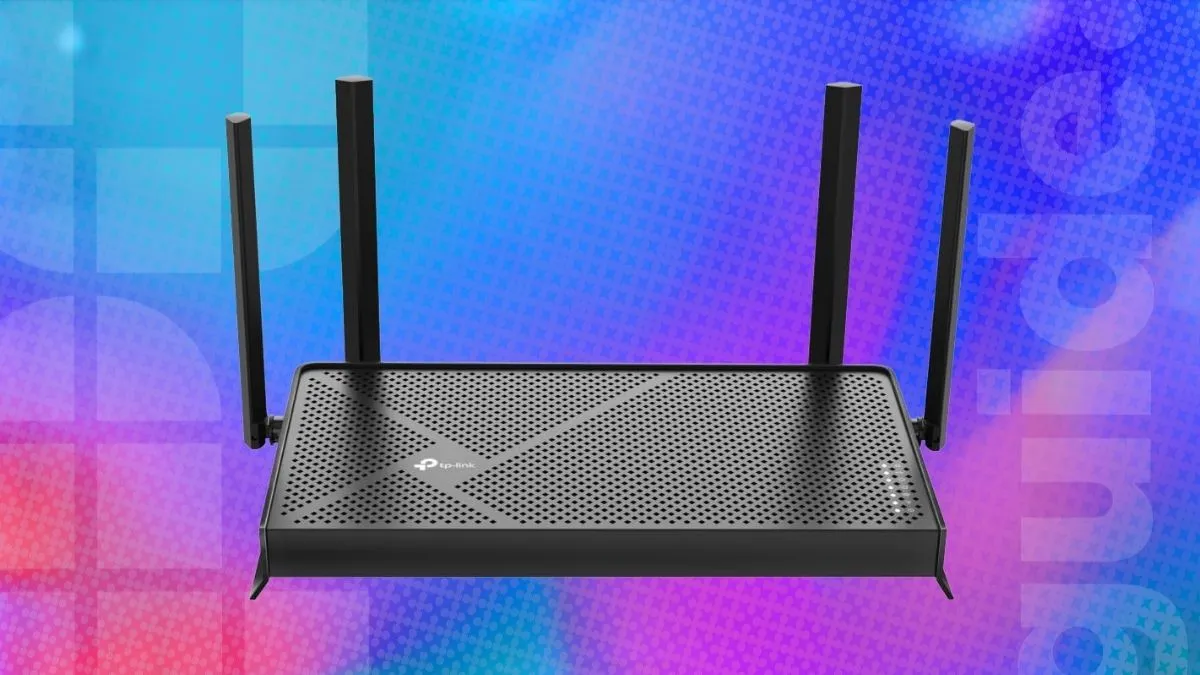
Amazon deal has shaved 33% off this popular TP-Link WiFi 7 router - PC Guide
Upgrading to a WiFi 7 router just got easier PC Guide is reader-supported. When you buy through links on our site, we may earn an affiliate commission. Read More
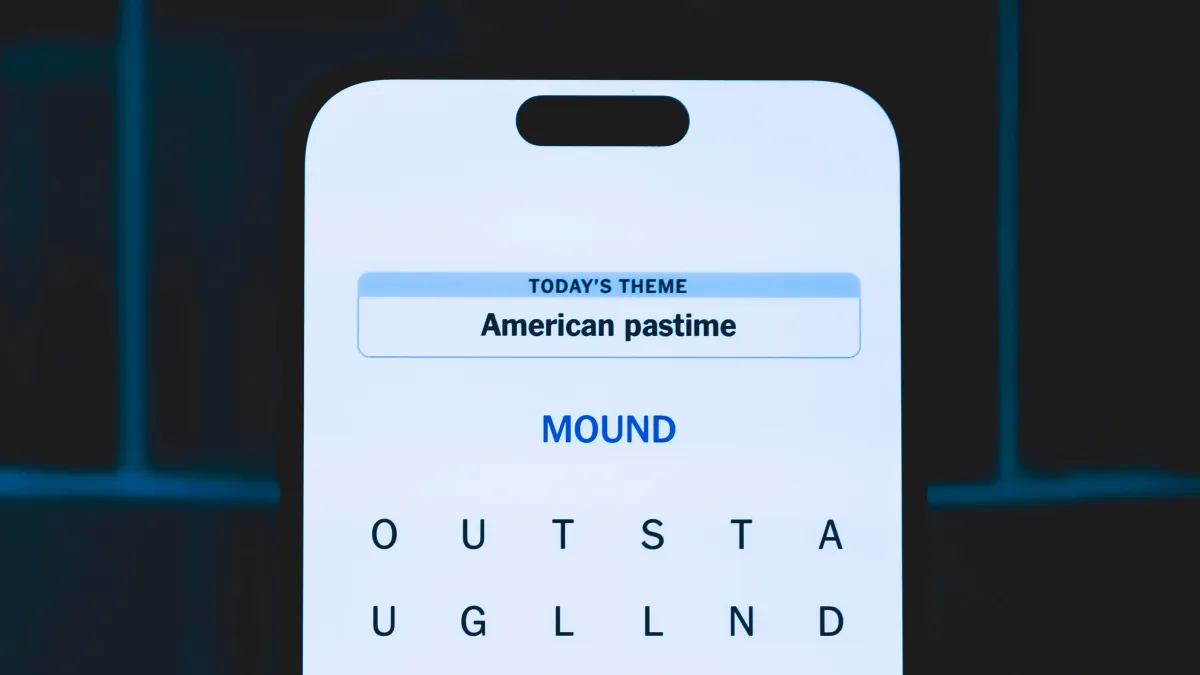
Today’s NYT Strands Hints, Spangram and Answers for Sunday, Oct. 18, #959 - CNET
Here’s your NYT Strands hint for today, plus the spangram and all of today’s Strands answers for puzzle No. 959 on Sunday, Oct. 18, 2026. Today’s Strands theme was tricky. It helps to be a runner. Read on for all the answers.
WARNING: ConnectWise Supply-Chain Attack Exposes Microsoft 365 Tenants - LinkedIn
A supply-chain attack involving ConnectWise’s cloud services has exposed Microsoft 365 customers to unauthorized application access, with researchers reporting successful sign-ins across 173 partner and customer tenants. The incident centres on credentials associated with ConnectWise Cloud Backup, formerly SkyKick, and raises concerns about attackers exploiting permissions already entrusted to business software. ConnectWise has confirmed unauthorized access to application identities within its Cloud Backup environment. In an October 17 update on its service-status page, the company said it was shutting off application access, interrupting customer backups while investigation and remediation continued.
0 comments
No comments yet. Be the first to share your thoughts!